
Know what you ship. Trust what you depend on.
Real-time SBOMs, exploit-aware risk scoring, and license compliance straight from your repos - direct and transitive dependencies tracked continuously, the noise filtered out.
Your SBOM tools are solving yesterday's problem.
Supply-chain attacks and regulatory pressure are rising - but most SCA and SBOM tools still flood you with noise, hide how they score risk, and miss the things enterprise reviews actually flag.
CVE dumps, not priorities
Traditional scanners report every CVE, creating noise and alert fatigue. You can't tell what's actually exploitable in your context - so real risks get buried.
Black-box classification
Commercial tools hide their scoring logic. You can't audit how a verdict was reached, customise thresholds, or fully trust the numbers in front of an auditor.
License & vendor blind spots
Copyleft licenses (GPL, LGPL) and third-party vendor risk - SLA expiry, breach history - surface late, usually mid enterprise review when they're most expensive.
Snapshots, not continuous
A point-in-time SBOM is stale the moment a dependency changes. Without continuous tracking, your inventory drifts out of sync with what you actually ship.
See your security posture in real time.
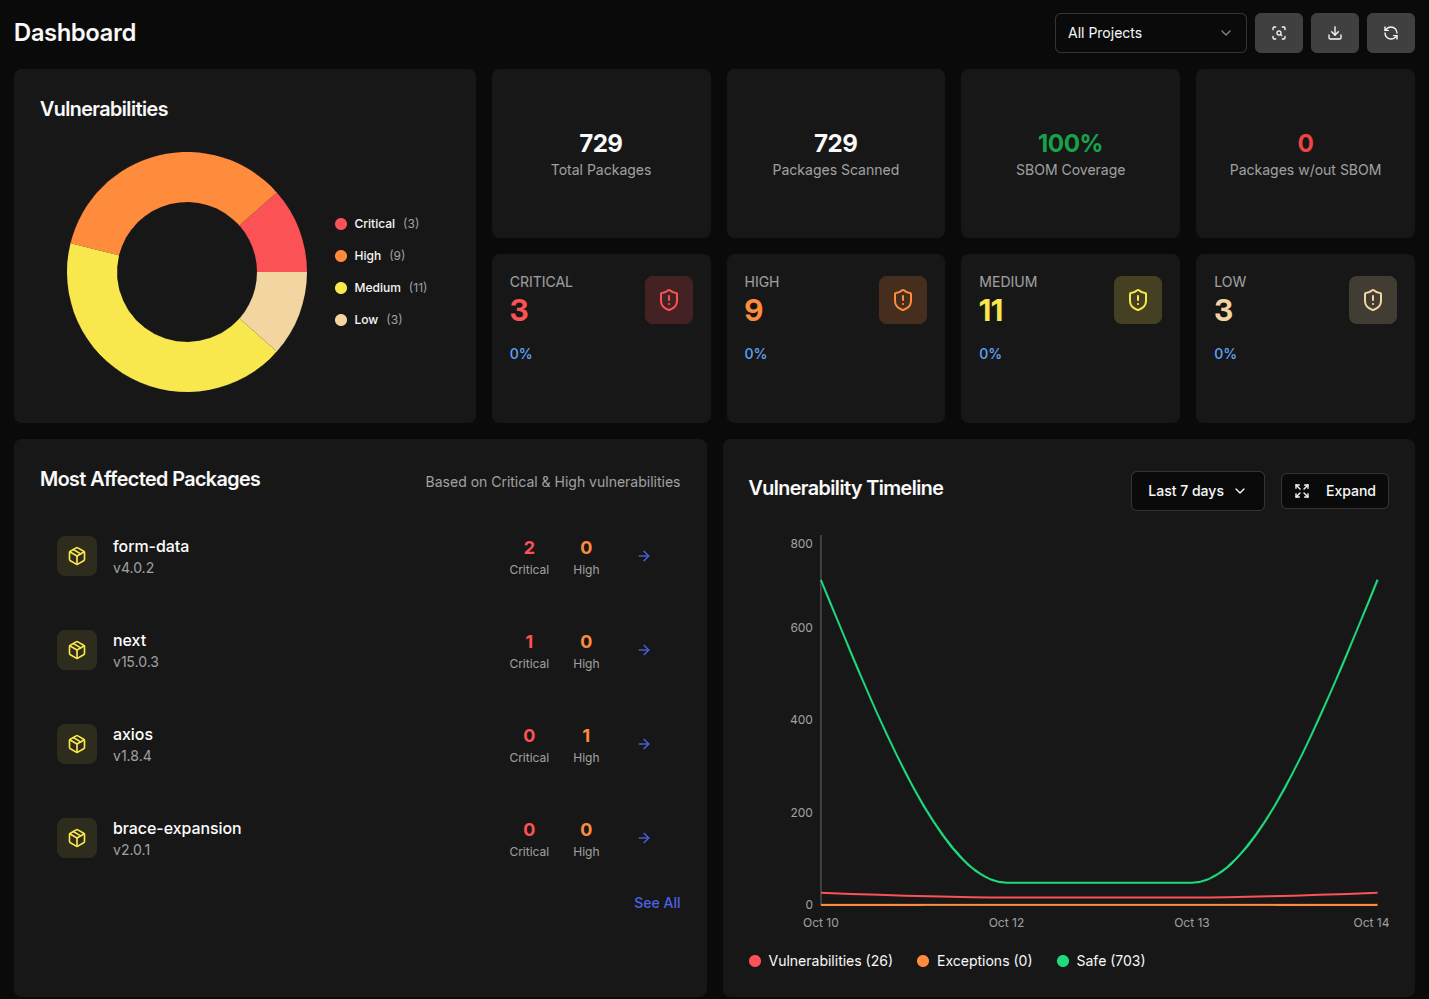
Connect a repo and Trace-AI generates a live SBOM, scans for exploitable risk, and validates license compliance - every package, every CVE, every version in one view.
See risk at a glance
Critical, High, Medium and Low exposure in one place - with a timeline and dependency network. Watch risk change as your code evolves.
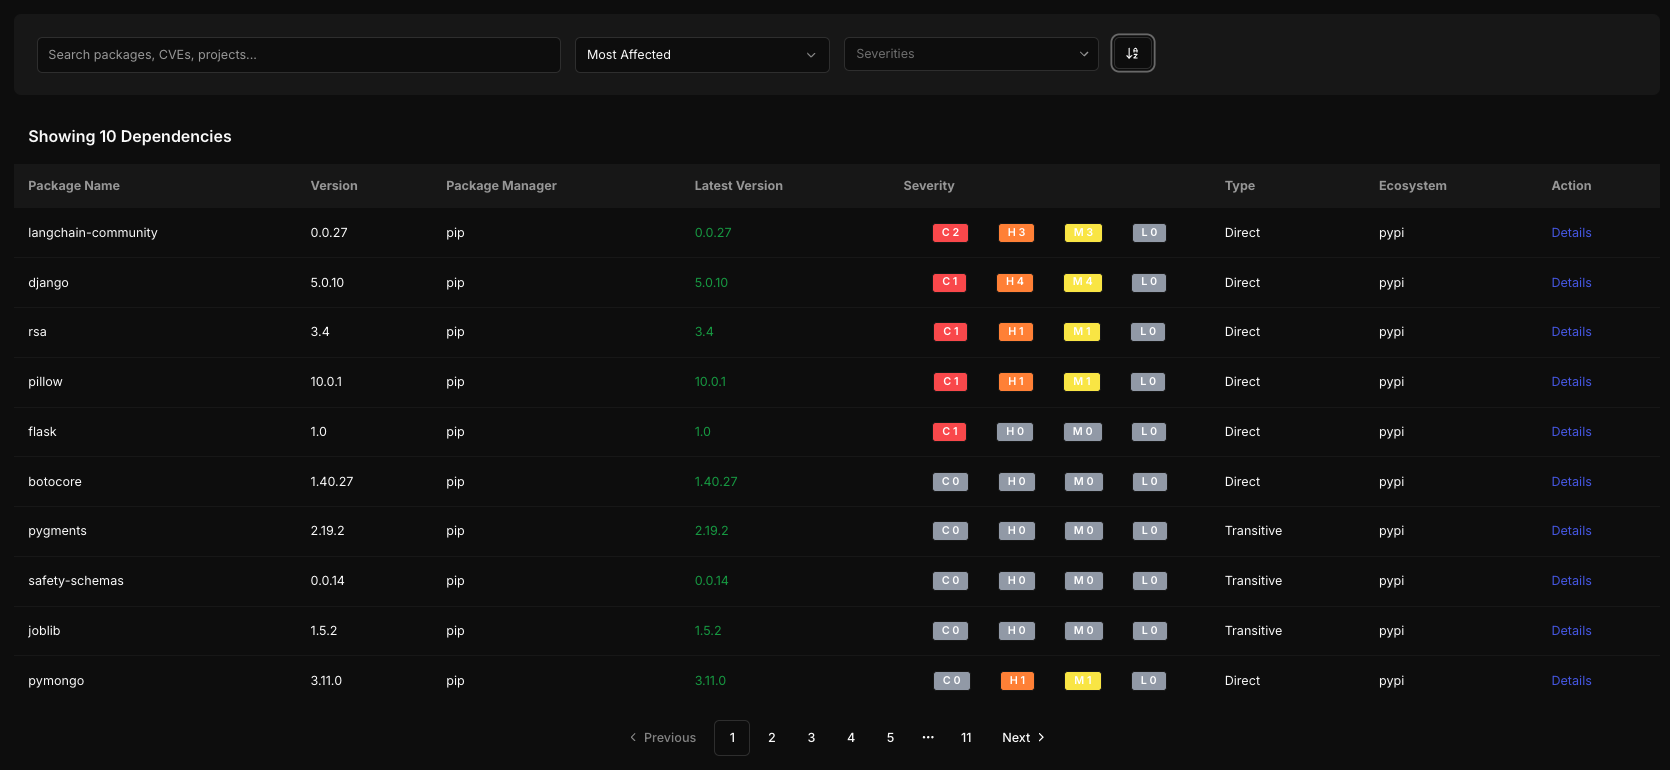
Clarity without the noise
Every package, every CVE and every version in one view. Direct vs transitive, severity tags, and project context - no black box. Built for developers.
License compliance made simple
Identify GPL, LGPL and other copyleft licenses instantly. Avoid surprises during enterprise review with a clear license distribution and policy library.
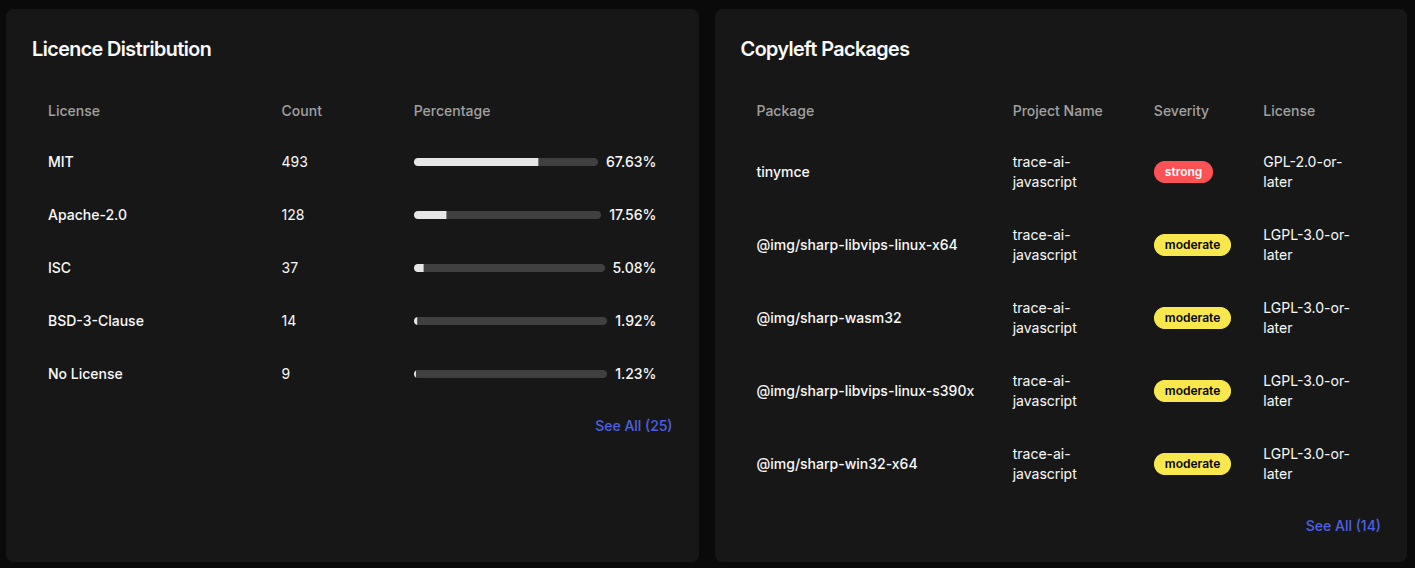
Real-time SBOMs
Accurate CycloneDX and SPDX straight from your CI. Direct and transitive dependencies tracked continuously.
Exploit-aware scanning
Move beyond CVE dumps. Prioritise what is actually exploitable in the wild and fix with full context.
Vendor visibility
Track APIs, SDKs, SLA expiry and breach history alongside your code dependencies.
Open-source transparency
We publish everything. Trace-AI is not a black box - ZSBOM is open and auditable.
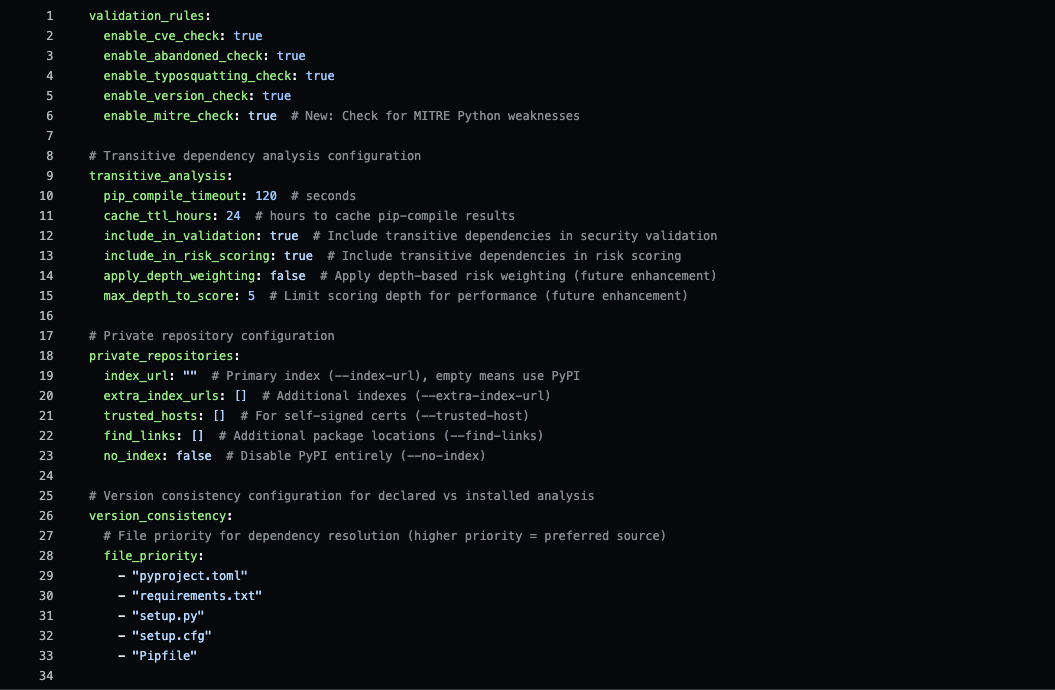
Built for what other SBOM tools miss.
Comparison reflects typical capabilities of legacy SCA and SBOM tooling; specifics vary by vendor.
Questions about SBOMs?
What an SBOM is, how exploit-aware scanning differs from CVE dumps, which ecosystems we support, and how your data stays secure - all answered.