Compliance Matters: Unlocking Revenue Through Privacy Maturity for SaaS Providers
Your Customers Expect Privacy-Are You Meeting Their Expectations? Imagine losing a high-value client because your privacy practices didn’t align with their expectations. A staggering 78% of consumers prefer companies that prioritize data privacy. In today’s digital landscape, trust isn’t optional it’s a competitive advantage. The question is: are you leveraging privacy to drive revenue and customer loyalty? The Privacy Maturity Model for SaaS Providers Privacy isn’t a one-time effort it’s a...
Your Customers Expect Privacy-Are You Meeting Their Expectations?
Imagine losing a high-value client because your privacy practices didn’t align with their expectations. A staggering 78% of consumers prefer companies that prioritize data privacy. In today’s digital landscape, trust isn’t optional it’s a competitive advantage. The question is: are you leveraging privacy to drive revenue and customer loyalty?
The Privacy Maturity Model for SaaS Providers
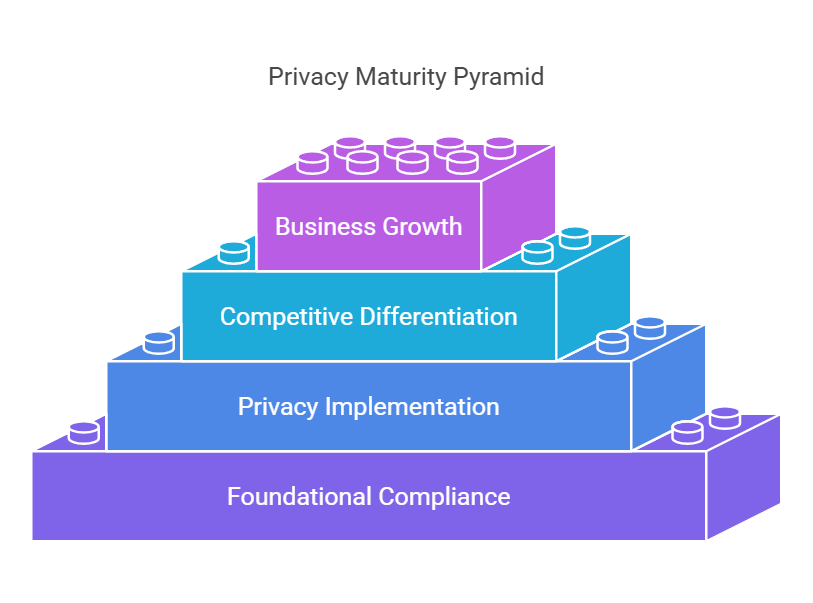
Privacy isn’t a one-time effort it’s a continuous evolution. SaaS providers should focus on four key stages of privacy maturity:
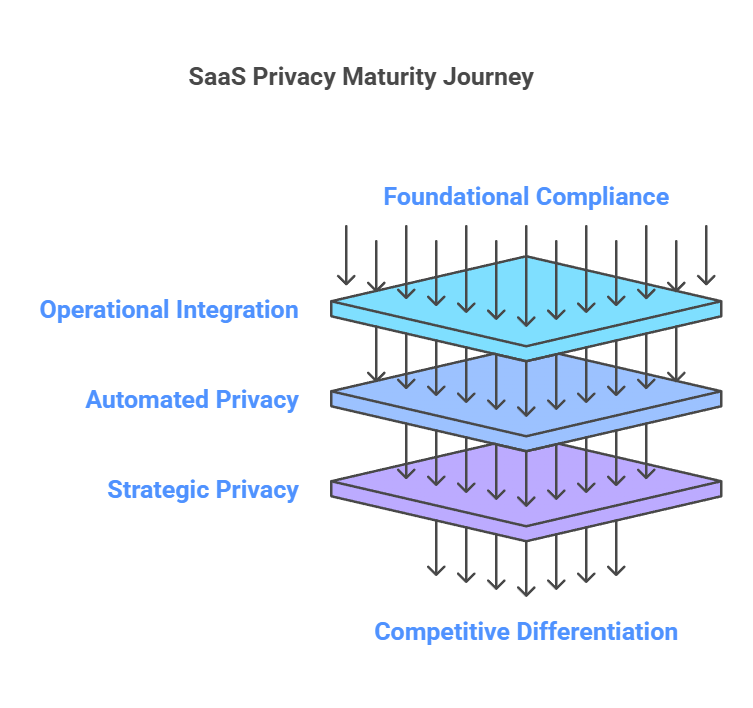
Stage 1: Foundational Compliance
- Meeting baseline legal and regulatory requirements (GDPR, CCPA, ISO 27701).
- Establishing privacy policies, data mapping, and consent management.
- Actionable Step: Conduct a comprehensive data audit this month to identify compliance gaps.
Stage 2: Operational Integration
Embedding privacy into engineering and business processes by ensuring Privacy by Design and Default.
Part 1: Privacy in Requirements & Design
- LINDDUN Framework: Used in GDPR-compliant privacy threat modeling to assess risks early.
- Data flow mapping: Minimizing data exposure across applications.
- Example: [Placeholder - A SaaS provider leveraging LINDDUN for privacy-first design.]
Part 2: Privacy in Engineering & Threat Modeling
-
Threat Modeling Frameworks for Privacy
-
STRIDE for SaaS environments to identify privacy risks.
- Integrating Data Minimization, Differential Privacy, and Pseudonymization at the code level.
-
-
Secure API & Data Processing Pipelines
- Reducing exposure in third-party integrations, AI models, and cloud storage.
- Example: [Placeholder - SaaS provider improving API security & privacy after a breach.]
Actionable Step: Schedule cross-departmental workshops to embed privacy considerations into product design by Q2.
Stage 3: Automated & Scalable Privacy
- Using automation to enforce privacy policies at scale.
- Privacy-Enhancing Technologies (PETs) as a Business Enabler
- Zero-Knowledge Proofs (ZKPs) for SaaS Security
- Implementation: Open-source ZKP libraries like ZoKrates and Aztec.
- Financial Services: ING Bank’s zero-knowledge blockchain system.
- Identity Verification: IDCrypt Global explores privacy-focused ID verification - though peer-reviewed validation is limited.
- Blockchain & DApp Integration: ZKPs are revolutionizing decentralized applications.
- Zero-Knowledge Proofs (ZKPs) for SaaS Security
Stage 4: Strategic Privacy & Competitive Differentiation
At this stage, privacy isn’t just about security it’s a market differentiator. Leading SaaS providers offer privacy-enhancing features like zero-knowledge encryption, decentralized identity management, and differential privacy.
How Transparency Fosters Business Growth
- Users trust SaaS providers who disclose data handling, retention, and privacy policies.
- Balancing feature personalization vs. privacy-first experiences.
- Example: Apple’s App Privacy Labels vs. Meta’s user tracking policies a transparency showdown.
Implementing Privacy as a Business Enabler
1. Privacy Engineering Practices
- Implement differential privacy & pseudonymization in analytics.
- Minimize data collection to reduce risk.
- Ensure end-to-end encryption (E2EE) in communications.
2. Automated Privacy Governance
- Deploy compliance automation tools for real-time monitoring.
- Enable self-service privacy controls for users.
- Automate Data Subject Rights (DSR) requests for GDPR & CCPA compliance.
3. Privacy-Focused Partnerships
- Collaborate with privacy-first cloud providers.
- Engage regulatory bodies to stay ahead of compliance updates.
- Work with independent auditors to validate controls continuously.
The Road Ahead: Privacy as a Growth Lever
SaaS providers that embed privacy-first strategies will not only avoid compliance risks but will gain a competitive edge, unlock new revenue streams, and strengthen customer trust.
Key Takeaways
✅ Privacy Maturity = Business Growth - Trust converts into loyalty & revenue.
✅ Four Stages of Maturity - Move from Foundational Compliance to Competitive Differentiation.
✅ Actionable Privacy Steps - Audits, PETs (ZKPs, AI-driven governance), & privacy-by-design.
✅ Transparency Wins Customers - Privacy-first SaaS providers outperform competitors.
✅ Automate & Scale - Compliance monitoring, encryption, and AI-driven privacy governance ensure success.
**The Next Step: Join the Private Beta for **Zerberus.ai
🔹 Want to automate privacy compliance without slowing down innovation?
🔹 Zerberus.ai is revolutionizing AI-driven privacy governance for SaaS providers.
🔹 Exclusive private beta access is open be among the first 100 testers!
🚀 Sign Up for the Zerberus.ai Private Beta Today! 🚀
Are you ready to turn privacy into a revenue driver? Download our free checklist on achieving privacy maturity today!